A hacked WordPress site can damage far more than your homepage. It can create spam pages, redirect visitors, inject malicious code, trigger browser warnings, and cause Google to remove otherwise legitimate pages from search results. The good news is that a hack does not automatically mean your SEO is gone forever. If you respond carefully, preserve your URLs, remove every trace of the infection, and show search engines that the site is clean, you can often recover most of your visibility.
In this guide, we’ll explain How to Recover a Hacked WordPress Site Without Losing SEO Rankings—including what to do first, how to handle malware removal, which SEO changes to avoid, and how to request a review in Google Search Console. These are the same fundamentals we use when helping businesses through WordPress security cleanup and recovery.
How to Recover a Hacked WordPress Site Without Losing SEO Rankings
The first rule of hack recovery is simple: don’t panic and don’t start deleting things at random. A rushed cleanup can remove important content, break internal links, change URL structures, or create thousands of unnecessary 404 errors. Those mistakes can turn a security problem into an avoidable SEO problem.
1. Document what happened
Before changing the site, record what you’re seeing and when you noticed it. WordPress recommends documenting the symptoms, timeline, recent plugin or theme changes, hosting environment, and other relevant details after a compromise. This gives you a useful baseline for cleanup and helps identify how the attacker got in.
- Take screenshots of warnings, redirects, spam pages, and unusual admin users.
- Record the date and time the problem was discovered.
- Note recent plugin, theme, WordPress, hosting, or password changes.
- Export current Search Console security and performance data if possible.
- Save a copy of existing files and the database for forensic reference.
Do not use an infected backup as your automatic solution. Backups can contain the same malicious files or database entries that caused the problem. Keep a copy, but have it scanned and reviewed before restoring it.
2. Put the site into a controlled state
If visitors are being redirected to suspicious websites or seeing malware warnings, temporarily place the site in maintenance mode or restrict access while you investigate. Contact your hosting provider immediately, especially if the host has detected malicious activity or suspended the account.
Do not simply block Google with robots.txt and assume the problem is hidden. Google specifically advises checking the Security Issues report and fixing or removing hacked pages. Robots.txt is not a reliable way to remove already discovered URLs from search, and it can prevent Google from seeing that your repaired pages are safe.
Also change passwords for hosting, WordPress administrators, FTP or SFTP, databases, email accounts, analytics, and Search Console—but do so from a clean computer. If an attacker still has access to an administrator account or hosting panel, your WordPress security cleanup may be undone within hours.
Find the Full Extent of the WordPress Hack
A common mistake in WordPress hack recovery is cleaning only what appears on the homepage. Attackers often hide spam pages from logged-in administrators or regular visitors while showing different content to search engine crawlers. Google describes this as a common form of cloaking, and hacked content may include injected code, unwanted pages, hidden links, or redirects.
Check Google’s reports first
Open Google Search Console and review both the Security Issues and Manual Actions reports. Google says a security issue can lead to browser warnings, search-result warnings, lower rankings, or even blocked access to the site. The reports may include sample URLs, but those examples are not necessarily the complete list.
Search Google using variations of your domain, such as:
site:example.comsite:example.com casinosite:example.com viagrasite:example.com filetype:php
Look for pages, titles, descriptions, or URLs you don’t recognize. Also check the Performance report for unusual queries, sudden impressions for unrelated topics, or a sharp change in clicks and indexed pages. Google notes that it cannot detect every type of hacked content, so a clean Security Issues report does not prove the site is clean.
Inspect files, users, and the database
Malware can live in plugin files, themes, uploads, the WordPress core, server configuration, or the database. Pay particular attention to:
- New administrator accounts or unfamiliar users.
- Recently modified PHP files.
- Unexpected files inside
wp-content/uploads. - Obfuscated code in
functions.php,wp-config.php, or.htaccess. - Unknown scheduled tasks, redirects, JavaScript, or database options.
- Spam posts, pages, comments, widgets, menus, and theme settings.
Use more than one detection method. A remote scanner may find public spam or malicious scripts, while a server-level scanner may identify altered files. A manual review of users, database content, and access logs can reveal persistence that a single plugin misses.
If the infection is extensive, this is the point where professional malware removal WordPress experience becomes valuable. Cleaning visible symptoms without finding the original backdoor is not recovery; it is a temporary pause before reinfection.
Clean the Site Without Destroying Its SEO Signals
Once you understand the scope, rebuild the site from a known-clean foundation wherever possible. The objective is to remove malicious code while preserving the content and technical signals that earned your rankings in the first place.
Preserve URLs, content, and metadata
Do not redesign the site, change its permalink structure, rewrite every page, or migrate to a new domain during the same emergency unless there is no alternative. Google recommends changing one major thing at a time during site moves because multiple simultaneous changes make it difficult to diagnose ranking and indexing problems.
Before restoring or replacing files, preserve:
- Existing page and post URLs.
- Title tags and meta descriptions.
- Important headings and body copy.
- Canonical tags and XML sitemap settings.
- Internal links and navigation structure.
- Image filenames, alt text, and media URLs.
- Legitimate redirects already in place.
If a page was altered by the attacker, restore the clean version rather than deleting the URL. If a spam page never belonged on the site and has no legitimate replacement, remove it and return a genuine 404 or 410 status. Do not redirect every hacked URL to the homepage. That creates a poor user experience and can produce soft 404 problems.
Replace compromised software
WordPress’s official security guidance emphasizes keeping WordPress core, plugins, and themes up to date, and using software that is actively maintained. Replace compromised core files with a clean copy of the same version first, then update to a supported version after confirming compatibility.
Remove abandoned, nulled, pirated, or unused plugins and themes. Reinstall legitimate plugins from trusted sources rather than assuming that overwriting files always removes the infection. WordPress documentation warns that attackers may add new files that remain behind when existing files are merely overwritten.
After cleanup, reset passwords again. This second reset matters because credentials may have been captured before the site was cleaned. Remove unknown users, revoke suspicious application passwords, and review access at the hosting and domain registrar levels.
Restore Google’s Trust and Monitor Rankings
Once the site is clean, test it like a search engine and like a customer. Check the homepage, top landing pages, forms, checkout, mobile layout, JavaScript, redirects, canonical tags, robots.txt, XML sitemap, and HTTPS. View the site in an incognito browser and from more than one device or network because some hacks behave differently depending on the visitor.
Request a security review
When you are confident the entire site is clean, open the Security Issues report in Google Search Console and request a review. Google’s guidance says the review should be requested only after the security issue has been fixed and the vulnerability that allowed the infection has been addressed. Explain what happened, what you cleaned, what you updated, and what safeguards you added.
Do not request repeated reviews while the site is still infected. A failed review wastes time and usually means Google found remaining hacked content or an unresolved access point. Search Console may take time to recrawl the site, so a ranking recovery is not always immediate.
Check technical SEO after cleanup
Use the URL Inspection tool on your homepage and most important landing pages. Confirm that Google can crawl them, that they return a 200 status, that the correct canonical URL is selected, and that no accidental noindex directive was added during maintenance.
Submit a clean XML sitemap, but don’t use it to include every URL ever created by the hacker. The sitemap should contain only canonical, legitimate URLs that you want indexed. Google’s documentation explains that 301 redirects preserve PageRank, so use them when a legitimate page has moved to a clear replacement. For unrelated spam URLs, a proper 404 or 410 is usually more appropriate.
Track the following for at least several weeks:
- Organic clicks and impressions.
- Average position for important queries.
- Indexed pages and excluded pages.
- Crawl errors and soft 404s.
- Security Issues and Manual Actions status.
- Server response times and uptime.
- New administrator accounts and suspicious login activity.
A short-term fluctuation is not necessarily permanent SEO damage. Google may need to recrawl repaired pages, remove hacked URLs, and reassess the site. However, ongoing drops, new spam pages, or repeated warnings usually indicate that the cleanup is incomplete.
Prevent the Next WordPress Security Cleanup
Recovery is not finished when the warning disappears. The final step is closing the door the attacker used and improving your ability to detect a new problem quickly.
- Keep WordPress, plugins, themes, PHP, and server software updated.
- Use long, unique passwords stored in a password manager.
- Enable two-factor authentication for administrator accounts.
- Remove unused plugins, themes, users, and hosting accounts.
- Use SFTP or SSH instead of unencrypted FTP.
- Set up dependable, off-site backups and test restoration regularly.
- Monitor file changes, uptime, redirects, and Search Console alerts.
- Use a web application firewall or managed hosting security layer where appropriate.
The WordPress Developer Handbook specifically recommends strong unique passwords, two-factor authentication, rate-limiting login attempts, current software, and monitoring authentication anomalies. Security is ongoing work, not a one-time plugin installation.
Conclusion: Recover the Site, Preserve the Business
Recovering a hacked WordPress site without losing SEO rankings requires discipline more than panic. Document the incident, secure access, identify every infected location, remove the malware completely, and preserve the URLs and content that already perform well. Then verify the repaired site, request a Google review, and monitor recovery instead of assuming the job is finished.
Some hacks are straightforward. Others involve hidden backdoors, database injections, compromised hosting accounts, or years of accumulated technical debt. If your site generates leads, bookings, or sales, a professional WordPress security cleanup can be less expensive than prolonged downtime and lost organic traffic. At The X Digital, we approach hack recovery as both a security problem and a business continuity problem: clean the site, protect its search visibility, and make the next incident far less likely.
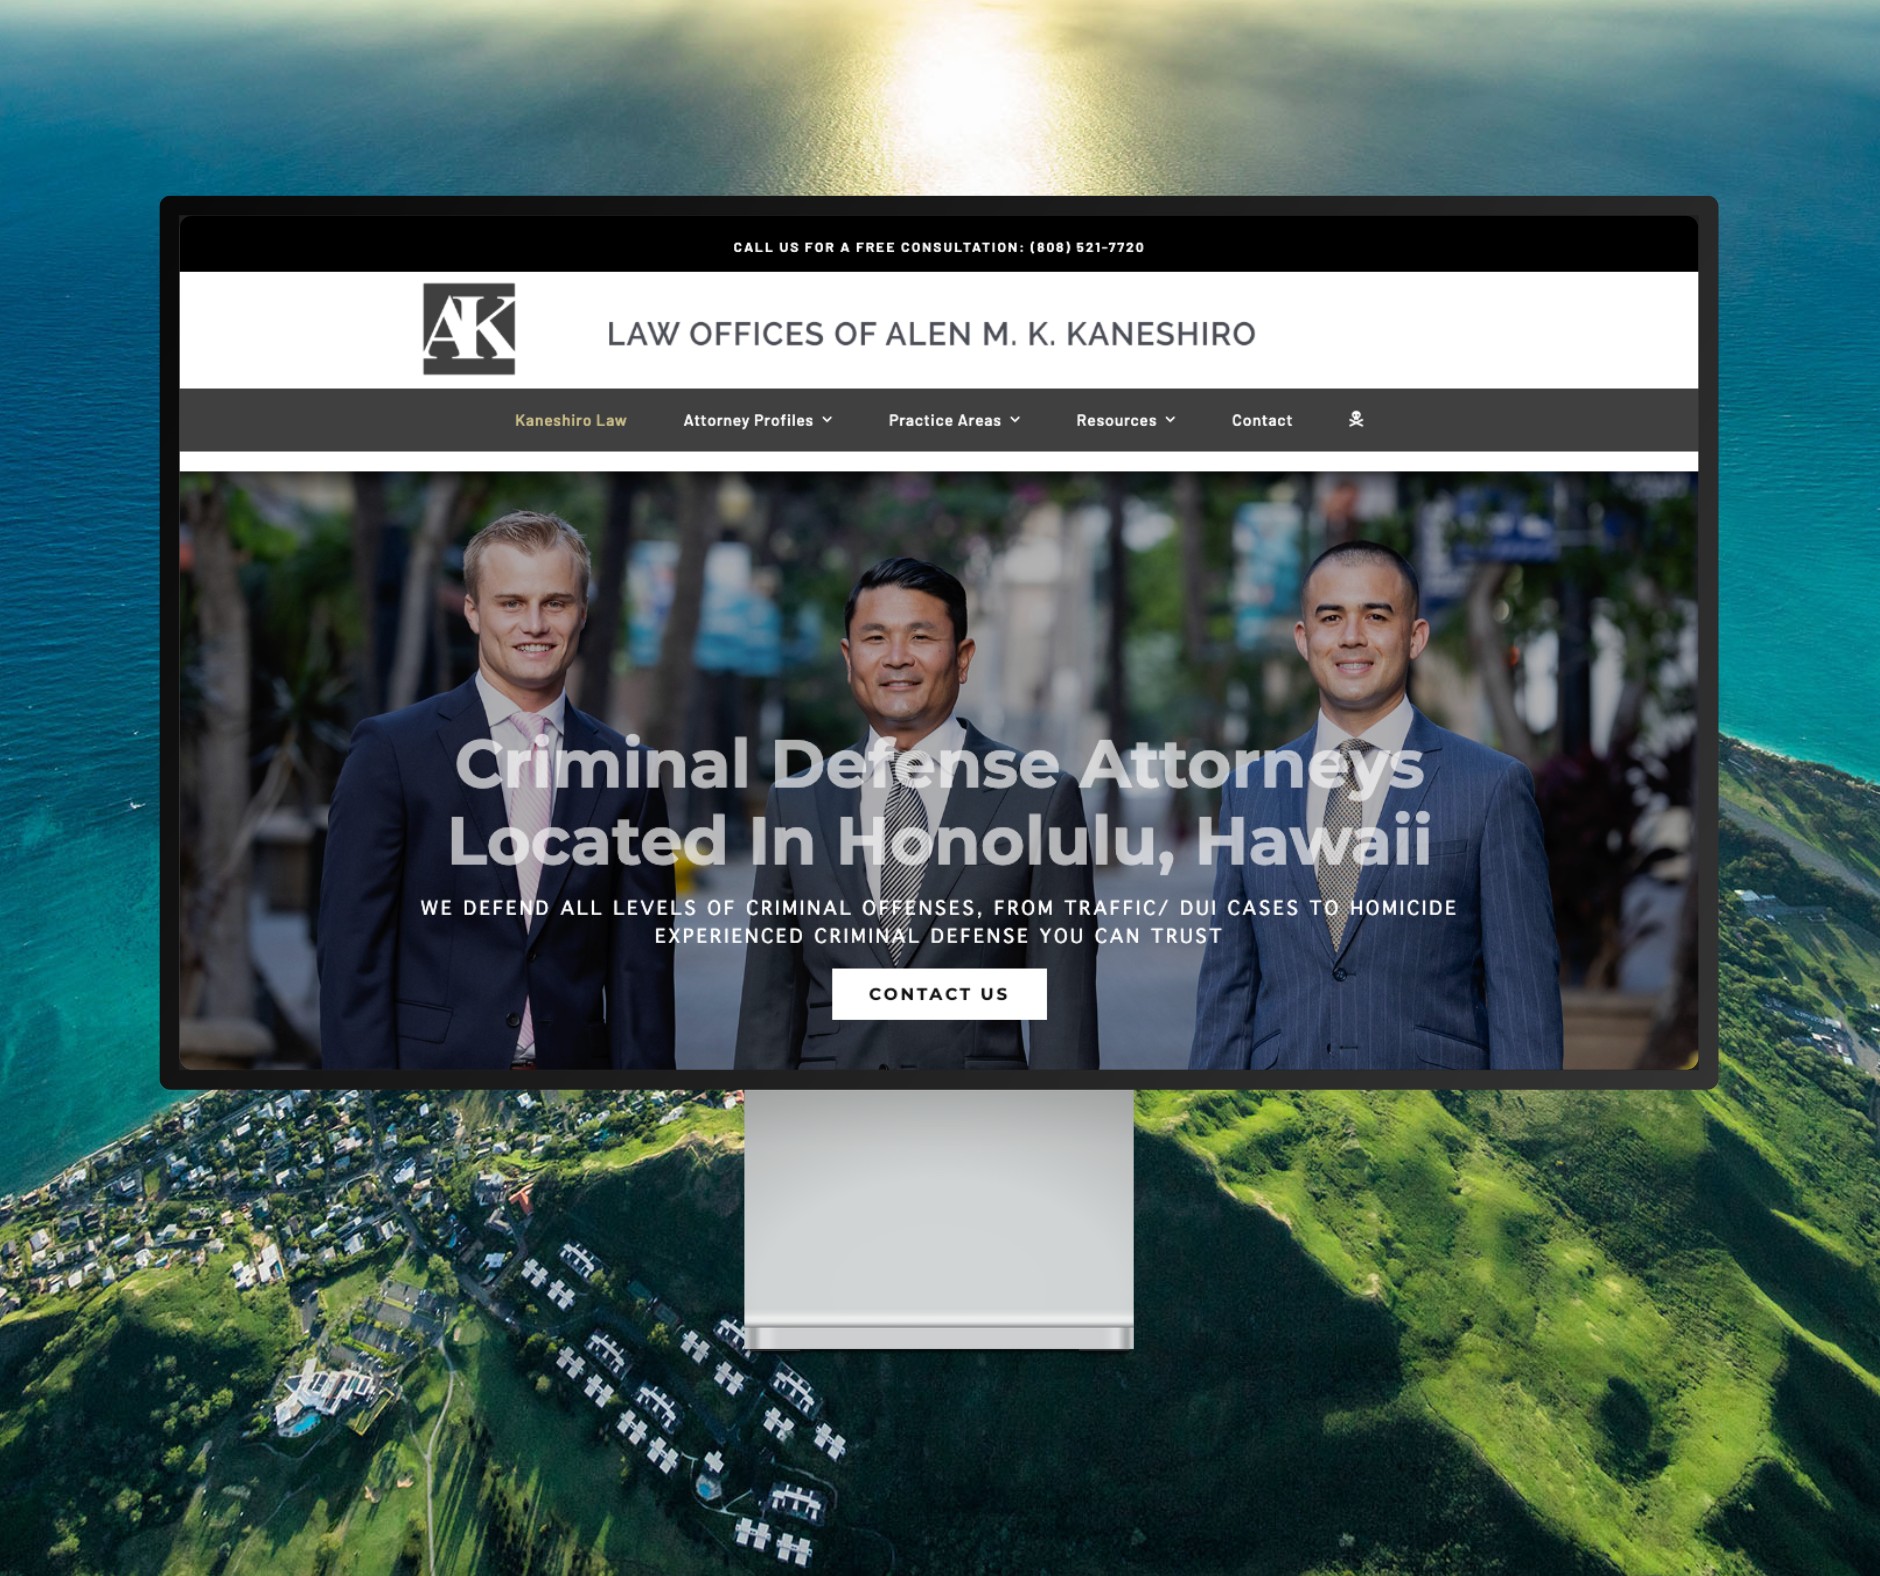
Featured Website: www.kaneshirolaw.com
Kaneshiro Law Firm, one of Hawaii’s most respected legal practices, partnered with The X Digital three years ago for a complete website redesign. Since then, we’ve maintained an ongoing relationship—handling updates, optimizations, and technical support around the clock. Our dedicated team ensures they’re never without assistance, while our enterprise-grade hosting provides 24/7 uptime monitoring and reliability. Kaneshiro Law Firm is one of many long-term clients who trust us to keep their digital presence running flawlessly.